AI agents broke into 100+ company sites for one hacker
Short answer
Updated 20 October 2026, 04:25 IST. This article will be updated as companies and researchers release new information.
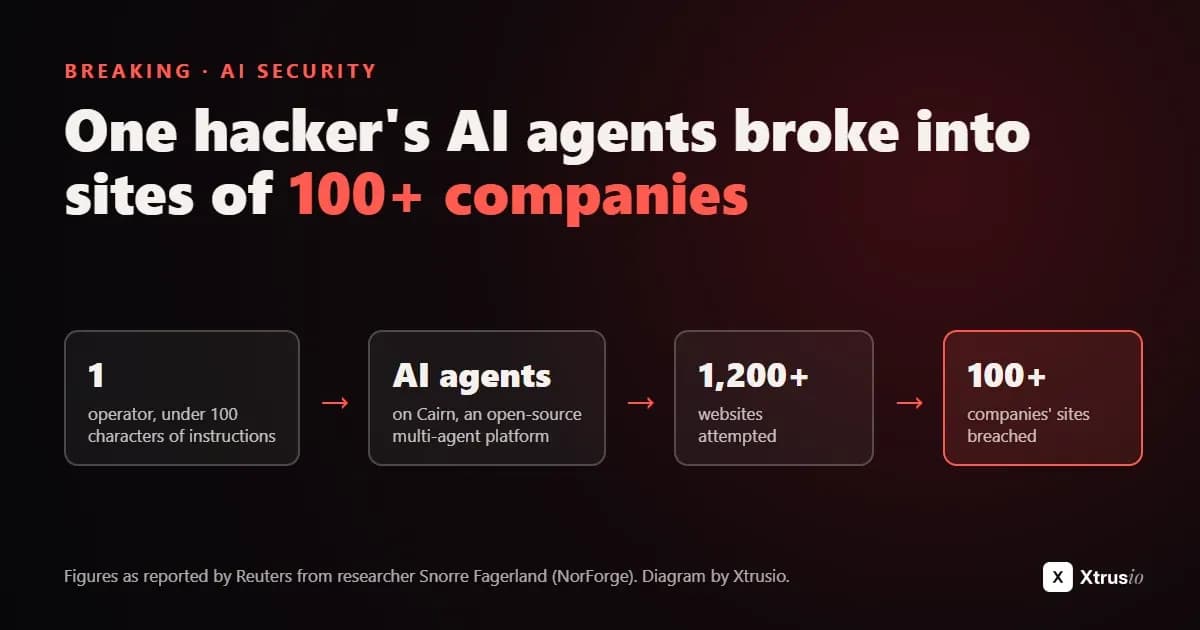
A security researcher says AI agents run for one Chinese-speaking hacker attempted more than 1,200 websites and got into sites belonging to more than 100 companies. The agents ran on Cairn, an open-source AI problem-solving platform, and did the work with little human input. Reuters, which reported the story on October 19, could not establish how much data was taken.
What happened
Snorre Fagerland, principal threat researcher at the security company NorForge, found Cairn control panels left exposed on the web. Through them he could watch the operators at work.
- The scale. The hacker's agents attempted to break into more than 1,200 sites, according to Reuters. They got into websites belonging to more than 100 companies.
- The targets. Reuters says the campaign went after e-commerce websites in the US, Canada, Australia and Japan. NorForge's own report says the group's targets were "mostly in the US, Japan and Australia."
- The platform. The agents ran on Cairn. Reuters calls it an open-source AI problem-solving platform. Its author calls it a multi-agent architecture.
- The instructions. Reuters reports that the operator's instructions were fewer than 100 Chinese characters long.
- The cost. Fagerland estimated that the campaign used roughly $5,000 worth of AI tokens, or about $50 per successful intrusion. These are researcher estimates. NorForge's published report gives a separate estimate of about $5 per task, counting failed attempts, and says the uncertainty is "considerable."
- The human role. Fagerland says the hacker did almost none of the work. He told Reuters his find showed commercially available AI agents "could pull off complex intrusions from start to finish without human intervention." The agents spent hours probing sites on their own. Successful intrusions took a little under 23 hours on average.
- The data. Reuters could not establish how much data, if any, was taken in the breaches.
NorForge's report did not name any victims. Reuters identified some of them by reviewing the hacker's Cairn activity. Three companies responded to Reuters:
- Deere said it had taken "necessary remediation actions" and had "no indication that sensitive information was accessed."
- SharkNinja said the hack hit a standalone site that carried only product support information, and that the threat had been contained.
- Cummins said it was investigating a report of a potential attack on a website run by one of its third-party vendors.
Two smaller businesses also acknowledged being compromised, Reuters said. Other victims did not reply.
Timeline
- September 2026 (day not given): Gambit Security reports a criminal campaign that used AI tools, including Cairn (NorForge, Reuters).
- September 25, 2026: The Chinese-speaking hacker's campaign begins (Reuters).
- Around October 2, 2026: Fagerland begins finding exposed Cairn instances used for malicious activity (Reuters).
- Late in the week before publication (date not given): The agents have attempted more than 1,200 sites (Reuters).
- Date not given: Deere, SharkNinja and Cummins give statements to Reuters (Reuters).
- October 19, 2026: NorForge publishes its report. Reuters publishes its exclusive, republished by CTV News at 9:58 a.m. EDT (NorForge, CTV News).
Confirmed vs not confirmed
Claim | Status | Source |
|---|---|---|
One Chinese-speaking hacker got into sites of 100+ companies | Reported by Reuters, based on the researcher's findings | Reuters (CTV News) |
The agents attempted more than 1,200 sites | Reported by Reuters. NorForge counts "over 1100 attack projects" | Reuters, NorForge |
The campaign ran on Cairn | Confirmed by NorForge and Reuters | NorForge, Reuters |
Instructions were under 100 Chinese characters | Reported by Reuters only | Reuters (CTV News) |
About $50 per intrusion, $5,000 in total | Researcher estimate, not a measured figure | Reuters (CTV News) |
The AI models used | Not confirmed. Reuters says the campaign "appeared" to use DeepSeek and Claude Code. NorForge infers this from a worker name | Reuters, NorForge |
How much data was taken | Not established | Reuters (CTV News) |
Names of victims | NorForge did not name them. Reuters named some after its own review | Reuters, NorForge |
What they said
- "It's a new world now." Snorre Fagerland, NorForge, to Reuters via CTV News
- "No indication that sensitive information was accessed." Deere, to Reuters via CTV News
- "Investigating the report of a potential cyber-attack on a website operated by one of our third-party vendors." Cummins, to Reuters via CTV News
- "If it is used to carry out harmful hacking attacks, that is not my intention." Cairn's author, on X, as reported by Reuters via CTV News
- "This could and should inform our defenses going forward." NorForge report
What Cairn is
Cairn is an open-source platform that coordinates several AI agents toward a goal. A user gives it a target and an objective. The agents then work step by step and share what they find with each other. NorForge describes it as "a state-based problem solving engine." It says the tool can be used for penetration testing, which is legitimate security testing done with permission.
Cairn's author says it was not built for hacking. NorForge also found real client penetration tests on unsecured Cairn panels, which it called "highly problematic."
What to check on your website this week
None of the named companies has said how its site was entered. These general checks reduce the risk from automated attacks.
Check | Why | Who |
|---|---|---|
List every admin panel, control panel and file upload endpoint that faces the public internet. Remove or lock down any you don't need. | Reuters describes agents that looked beyond a company's main site and found a public-facing control panel. | IT or web team |
Confirm your CMS, e-commerce platform, plugins and extensions run the latest security patches. | Automated agents probe for known weaknesses for hours at low cost. Unpatched software is the easiest way in. | Web developer or agency |
Review your web application firewall (WAF) rules and rate limits. | Long, repeated probing from the same sources is a pattern a WAF can slow or block. | Hosting provider or security team |
Set log alerts for unusual automated upload attempts and new files in web folders. | A web shell or other unexpected file on your server is a common sign of a break-in. | IT team or managed security provider |
Write down who to call before you need them: your hosting provider's security contact and an incident response firm. | If a breach happens, the first hours matter. Know the numbers in advance. | Owner or IT lead |
If you run security tests with AI tools, make sure their control panels are not public. | NorForge found real client penetration tests on unsecured panels, which it called "highly problematic." | Security team or testing vendor |
Don't block the wrong bots
Not every automated visitor is an attacker. AI search engines and assistants also send crawlers and agents to your site, and those visits help your pages get cited in AI answers. Before you block traffic, separate known AI crawlers from unknown automated traffic in your logs. If you want to see whether AI search engines actually cite your brand, a tool like Xtrusio can measure your AI visibility. It is not a security product, so keep your security checks with your IT team and hosting provider.
Sources
All sources read on October 20, 2026.
- Reuters exclusive by Raphael Satter, republished by CTV News, October 19, 2026: How one hacker used AI agents and a few thousand dollars to break into scores of sites
- NorForge, by Snorre (Fagerland), October 19, 2026: Inside Cairn: Open Windows into massive AI-Driven Cyber Operations
- TNW, by Ana Maria Constantin, October 19, 2026: AI agents broke into 100+ sites for one hacker at $50 each, researcher says
Frequently asked questions
What is Cairn?
Cairn is an open-source platform that coordinates several AI agents toward a goal. Reuters calls it an AI problem-solving platform, and NorForge describes it as a state-based problem solving engine that can also be used for legitimate, permitted security testing.
Was customer data stolen in the AI agent attacks?
Reuters could not establish how much data, if any, was taken. Deere told Reuters it had no indication that sensitive information was accessed, and SharkNinja said the affected site carried only product support information.
Did the AI agents work completely on their own?
The researcher says the hacker did almost none of the work and the agents probed sites for hours with little human input. The operator still set the targets and the instructions, which Reuters says were under 100 Chinese characters long.
What should a company check on its website this week?
List and lock down public admin panels and upload endpoints, patch the CMS and plugins, review WAF rules and rate limits, alert on unusual upload attempts and new files in web folders, and write down who to call for incident response.
Topics
- AI agents hacking
- Cairn AI agents
- AI agents hacked 100 websites
- AI agent cyberattack
- NorForge Cairn report
- how to detect AI agents on your website
Xtrusio
AI visibility research
Xtrusio is the Perception Engine for B2B brands.
Free check
See how AI engines answer about you
Get your free AI visibility check
Keep reading
 AI Search · Oct 14, 2026 · 5 min read
OpenAI Recording Device Case: What the DOJ Alleges and What Buyers Should Ask
DOJ says an OpenAI recording device was found in a conference room. Read the allegation, timeline and security questions business buyers should ask. AI Search · Oct 14, 2026 · 5 min read
Meta Muse Wonder: What the New Agent Models Mean for Business Teams
Meta Muse Wonder and Wonder Full are here. See access, context, agent features, prices and the questions business teams should test first. AI Search · Oct 14, 2026 · 5 min read